SonicWall warns an SSL-VPN MFA bypass flaw has been exploited
CVE-2026-19868 affects SonicOS SSL-VPN set up with SAML authentication.
Leaked on 07 November 2026
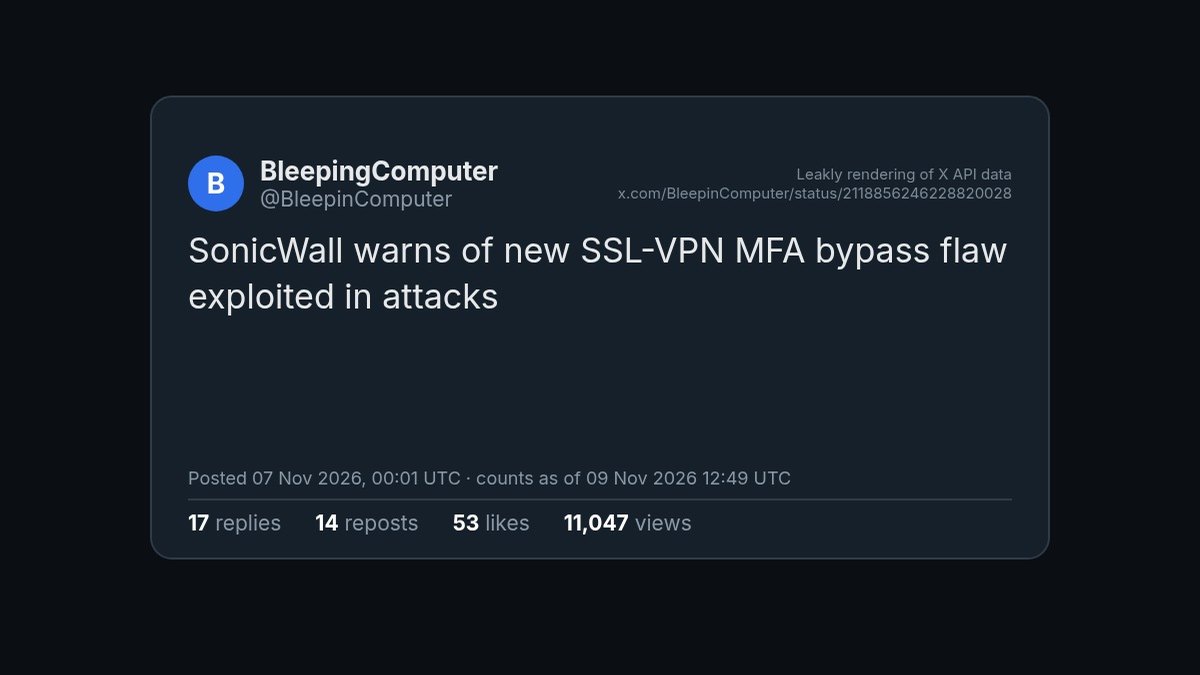
SonicWall released updates for seven SonicOS vulnerabilities, including an SSL-VPN authentication bypass flaw exploited in attacks, BleepingComputer (@BleepinComputer) reported on November 7.
The flaw, CVE-2026-19868, lets attackers with valid credentials for an alternate authentication method bypass SAML controls, potentially including SAML-enforced MFA. It has a CVSS score of 7.1, according to BleepingComputer.
SonicWall confirmed a report of potential exploitation and urged customers to upgrade.